Improve email security on your domain
Stop criminals sending fake invoices from your domain. How SPF, DKIM and DMARC protect your clients and staff from email impersonation, in plain language.
· Updated · 3 min read
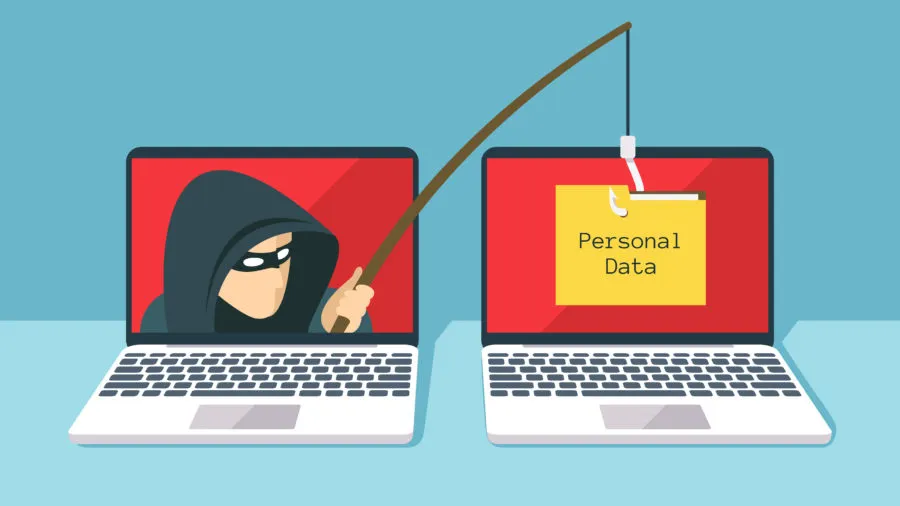
An email address on your own domain shows people you’re a real business. On its own, though, it doesn’t stop criminals from sending email that looks like it came from you.
Take a typical accounts department. The people who work there are used to sending and receiving sensitive financial information like customer invoices, bank statements, proofs of payment and supplier invoices.
By impersonating someone from your accounts department, an attacker can send your clients fake invoices, fake banking details and fake requests to log in and reset their passwords on a compromised website.
With the right settings on your domain, most of this risk goes away, because the recipient’s email service can check that email from your domain really came from you.
You don’t need to understand the technical details for this to work. We set it up for you. If you’d like to know how it works, read on: it’s standard good practice, not obscure technology.
We use three standard settings: SPF, DKIM and DMARC. They live in your domain’s DNS, the settings that tell the rest of the internet where to find your website and deliver your email.
What is SPF?
SPF is short for Sender Policy Framework. An SPF record lets other servers know which networks and servers can be trusted to send email on behalf of your domain.
When you send an email, the recipient’s mail server checks the message headers to verify that it came from an approved source. If it fails this check, the email may be treated as suspicious, labelled as spam or blocked outright. Email that passes the SPF check is delivered as legitimate email from a legitimate source.
All you need to activate SPF on your domain is a TXT record in your domain’s DNS configuration.
An SPF record that tells servers to trust email from Google (Gmail) looks something like this:
v=spf1 include:_spf.google.com ~all
SPF is commonly used together with another email verification technology called DKIM. Having both enabled on your domain greatly improves security and email deliverability.
What is DKIM?
DomainKeys Identified Mail (DKIM) lets organisations take responsibility for the messages they send and guarantee their contents. This helps prevent spoofing, where email content is changed to make a message appear to come from someone or somewhere other than the actual source.
DKIM adds a digital signature to the header of every outgoing message. Email servers that receive these messages use the public DKIM key published in your DNS to check the signature, which proves the message came from your domain and wasn’t changed after it was sent. You can learn more about DKIM at dkim.org, where the group that developed the standard has published detailed explanations, how-tos and news.
Once SPF and DKIM are configured on your domain, you need to tell other mail servers how to react when an email from your domain fails either check.
What is DMARC?
Domain-based Message Authentication, Reporting and Conformance (DMARC) isn’t an email authentication protocol itself, but it builds on the key authentication standards, SPF and DKIM.
DMARC lets an organisation publish a policy that defines its email authentication practices and tells receiving mail servers how to enforce them.
To enable DMARC, you add a TXT record to your DNS configuration. First make sure that both SPF and DKIM are configured for your domain.
Here’s an example DMARC policy that rejects 100% of messages that fail the DMARC check and emails a daily report to two addresses:
v=DMARC1; p=reject; rua=mailto:postmaster@domain.com, mailto:admin@domain.com
Check your domain
If you’ve had fake email sent in your name, or you’re not sure these settings are in place, send us your domain name and we’ll check it for you.
Ask us to check your domain. The check is free, and we’ll tell you what’s missing and how to fix it.